NIS2 in healthcare: what IT teams must instrument
NIS2 operational evidence pack for a health IT team: Art. 21 and 23 of Directive (EU) 2022/2555, 24/72/one-month clocks, ANSSI and CERT-FR, and the dual-channel GDPR.
Ala Ben Aicha
Direct answer
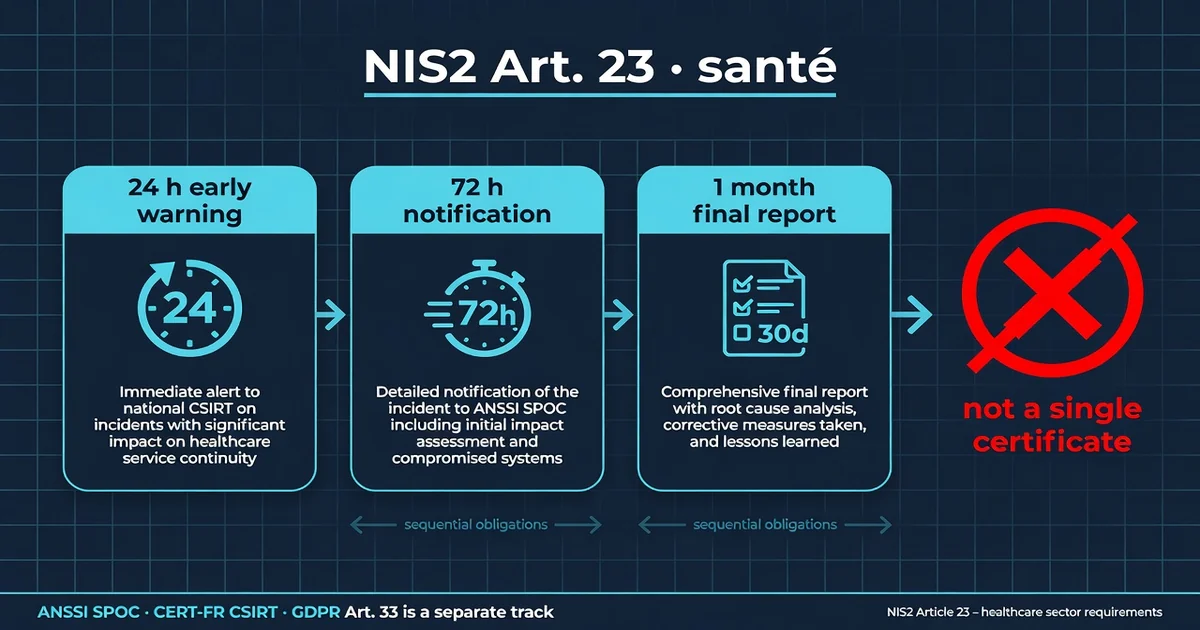
NIS2 is not a single certificate. For an essential or important entity, article 23 imposes 24 hours, 72 hours then one month. In France, ANSSI is the point of contact; the Commission still noted in 2025 an incomplete transposition.
A directive, not the EHDS / MDR / GDPR stack
The page EU healthcare compliance cartography four diets. This isolates NIS2 for the team that must instrument detection, escalation and proof. Pinch text: directive (EU) 2022/2555 (NIS 2). Transposition deadline: October 17, 2024; national measures applicable from October 18, 2024.
The sector of health appears in Annex I. This does not automatically make any publisher, host or firm essential entity. Type of entity, size (thresholds in the annex to Recommendation 2003/361/EC, included in art. 3), specific inclusions and national transposition law count. A CISO does not “declare” the status in a README: it is an organizational decision, with legal advice.
Incident clocks: NIS2 Art. 23 is not GDPR Art. 33
Thesection 23 (ELI) imposes, for a significant incident, notification to the CSIRT team or the competent authority. The letters below are those of art. 23(4); 24 hour / 72 hour / one month clocks remain the default delays of (a), (b) and (d):
| Clock | Deadline (directive) | Recipient (directive) | Minimal content | What it is not |
|---|---|---|---|---|
| Early warning | 24 hours after knowledge — Art. 23(4)(a) | CSIRT / authority | Significant incident; suspected unlawful or malicious act? ; cross-border impact? | An internal Jira ticket, a Slack post-mortem |
| Incident notification | 72 hours after knowledge — Art. 23(4)(b) | ditto | Update of (a) + initial assessment (severity, impact, IoC if available) | The notification GDPR |
| Interim report | On request of the CSIRT / of the authority — Art. 23(4)(c) | ditto | Relevant situation updates | A final report “in advance” |
| Final report | One month later (b) — Art. 23(4)(d) | ditto | Detailed description (severity, impact); type of threat or probable root cause; mitigation measures applied and ongoing; cross-border impact if applicable | An ISO 27001 certificate; art. 23(4)(c) |
| If the incident is still in progress to (d) | Progress report at that moment, then final report one month after treatment — Art. 23(4)(e) | ditto | (e) does not merge with (c): (c) is a request for authority; (e) is the “always open to (d)” case | A silence “we’ll see on Monday” |
| GDPR Art. 33 | 72 hours (lane distinct) | Data Protection Authority | Personal data breach at risk | An NIS2 substitute |
(c) is not the one-month report. (d) is the final report, one month after notification (b), not a month after acquaintance. (e) is not “on request if it lasts”: if the incident is still open at the time of (d), you file a progress report instead of the final (d) at this deadline, then a final one in the month following the treatment.
The two 72 hours can coincide on the calendar and differ on the recipient and the content. In France, the NIS2 route targets the CSIRT / designated authority; the GDPR route targets the CNIL. A single “we had an incident” email doesn’t satisfy either of us.
Trusted service providers: derogation from point (b) of art. 23(4) — notification 24 hours (not 72 hours) for the significant incident which impacts the trust service. Do not copy this exemption onto a hospital DPI.
France: ANSSI, CERT-FR, and what the Commission actually wrote
The Commission page “NIS2 implementation in France” (updated July 7, 2025) indicates:
- May 7, 2025 : reasoned opinion for failure to notify complete transposition.
- Single point of contact: ANSSI (
[email protected]). - National CSIRT: CERT-FR (contact 24/7).
I am not inventing the name of a “definitive” French law here. As long as the Commission publishes a reasoned opinion for incomplete transposition, a slide “we are transposed, therefore we are compliant” is a risk, not proof. Read the national text in force on D-Day with your counsel, and keep the Commission URL in the evidence file along with its date of consultation.
Art. 21: ten families of measurements, one audit trail per family
Article 21(2) lists measures proportionate (not a miracle product):
| Letter | Family Art. 21(2) | Engineering proof (example) |
|---|---|---|
| (a) | Risk analysis and IS security policies | Versioned risk register, named owner |
| (b) | Incident management | Runbook 24/72/1 month + dated exercise |
| (c) | Continuity, backup, recovery, crisis | Restoration exercise with measured RTO/RPO — not a PDF policy |
| (d) | Supply Chain Security | Supplier inventory + clauses + tipping test |
| (e) | Acquisition/development/maintenance, vulnerabilities | SDLC, CVE management, documented patch window |
| (f) | Effectiveness assessment | Audit / intrusion test planned, not a marketing badge |
| (g) | Cyber hygiene and training | Proof of training of the management body (Art. 20) |
| (h) | Cryptography | TLS / keys / HSM inventory, not “we have HTTPS” |
| (i) | HR, access control, assets | Dated access review, minimal CMDB |
| (j) | MFA, secure communications | MFA on EHR Admin and on the incident climbing path |
Article 20 charges themanagement body. A single CISO who “signs NIS2” in Confluence is not Art. 20.
Integration exercise (without real data)
In a test environment, cut a downstream system (HL7 queue, FHIR API, or Mirth destination). Time: detection, classification “significant?” », 24-hour alert (draft to the internal box, not to CERT-FR), queue growth, recovery, reconciliation. The hole this exercise reveals — absent owner, no clock, no IoC — is the backlog item. Do not report a fictitious incident to the authority.
The English version, without ANSSI as if it were valid for all Member States, is NIS2 for healthcare IT teams.
What this page is not
It is not an essential entity qualification, not an ANSSI opinion, not a substitute for legal advice, not an ISO audit, not clinical advice. I do not notify for you. The health data architecture under GDPR remains a construction site separate.
If you need to instrument logs, files and toggles around care interfaces, it's interoperability in digital health. For a bounded spike, use the contact with project intention.